

On September 18, the PwC Japan Group announced that, ahead of the implementation of the "Supply Chain Measures Assessment System," it would begin offering a quick assessment service to support companies in their compliance with the system.
<Overview of the "Supply Chain Measures Evaluation System">
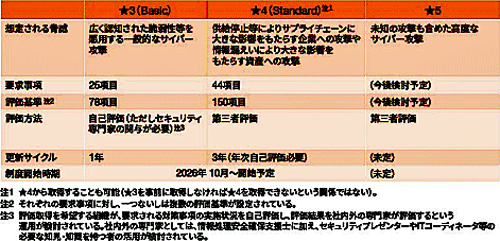
The "Supply Chain Security Measures Evaluation System" is a security measures evaluation system for strengthening supply chains that the Ministry of Economy, Trade and Industry plans to launch in fiscal year 2026 to evaluate the level of cybersecurity measures taken by supply chain companies (companies receiving orders).
The supply chain security assessment system will target IT infrastructure such as PCs, servers, network equipment, and cloud services, setting tiered levels of security measures and clarifying the cybersecurity measures required at each level. Specifically, draft security measures and evaluation criteria have been presented for two levels: ★3 Basic, which can deal with general cyber threats, and ★4 Standard, which can deal with attacks on companies that have a significant impact on the supply chain. The system is expected to be implemented during fiscal year 2026.
<Overview of Quick Assessment Services>
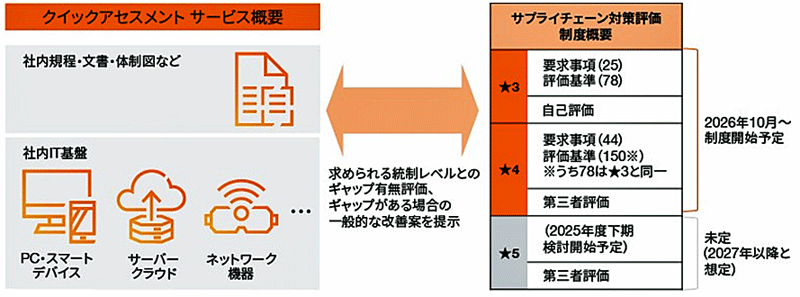
PwC Japan's new Quick Assessment service analyzes whether there are any gaps between a company's cybersecurity measures and the evaluation criteria (★3 Basic and ★4 Standard) published by the Ministry of Economy, Trade and Industry. It then provides companies with general improvement suggestions, such as revising internal regulations and changing IT infrastructure settings. This allows companies aiming to obtain certification under the Supply Chain Security Assessment System to objectively evaluate their current level of preparedness even before the system is implemented and prepare necessary cybersecurity measures early on. This enables them to pinpoint their countermeasures and leads to cost reductions.
Furthermore, for companies that have used the Quick Assessment, we will continuously monitor any gaps between their current performance and the standards required by the Supply Chain Security Assessment System, even after the system has been implemented, to support them in obtaining certification. We also plan to offer a service that proposes countermeasures such as changing IT infrastructure system settings in response to revisions to the system or changes in the business environment of companies.
Under the supply chain security assessment system, ordering companies are expected to encourage receiving companies to implement appropriate cybersecurity measures based on industry characteristics and anticipated risks, through transaction contracts and other means. Receiving companies can expect benefits such as building trust with their business partners and expanding business opportunities by obtaining certification under the supply chain security assessment system.
In recent years, companies involved in supply chains have increasingly become targets of cyberattacks, necessitating the development of robust cybersecurity measures. Challenges include the difficulty for ordering companies to assess the security measures of individual companies from the outside, and the fact that receiving companies are required to meet varying levels of security measures from their business partners. Therefore, the Ministry of Economy, Trade and Industry has been considering the introduction of a supply chain security evaluation system to visualize and strengthen the level of cybersecurity measures for receiving companies.


